What changed
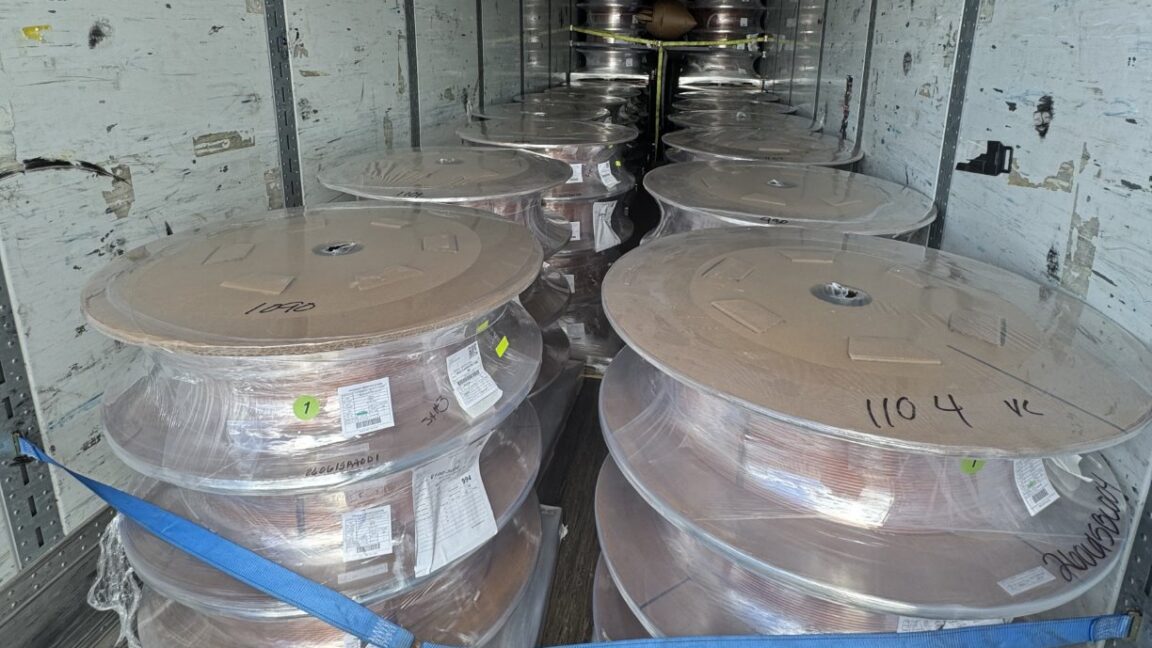
Highway thieves have reportedly stolen more than $100 million in data-center freight since June by combining freight-account compromises, fake driver identities, malicious links and GPS spoofing. The targeted cargo included servers, fiber-optic cables, memory chips, copper wire and cooling equipment; two unrecovered shipments were valued at about $13 million and $10 million.
Why it matters
This is a supply-chain attack with wheels on it. Thieves reportedly compromised freight brokers’ accounts, used fake listings to contact trucking companies, installed software through malicious links and then redirected legitimate shipments. In some cases, real drivers collected the cargo without knowing the plan before it was handed to accomplices.
The digital layer also defeated physical security. In one case, a sedan struck the vehicle of two off-duty police escorts while a trailer carrying $13 million in server equipment drove away. Another shipment, carrying roughly $10 million in server-rack components, escaped after an SUV hit its escorts, even though an app was monitoring the cargo’s location. The coordinates were apparently spoofed.
The losses are not limited to finished computing hardware. Illinois investigators recovered about $300,000 in copper wire and roughly $1 million in custom data-center power equipment. Another recovered trailer contained cooling equipment alongside nicotine pouches, televisions, shoes, printers, speakers and skin-care products.
The immediate lesson is uncomfortable: a shipment can be authenticated, tracked and physically escorted, yet still be vulnerable when the broker’s account, driver identity or location data has been compromised. The full number of thefts and their eventual effect on data-center construction remain unclear, but the reported cases show that logistics software is now part of the attack surface.
Comments
No comments yet.